Exhibit L · 04 Sept 2026
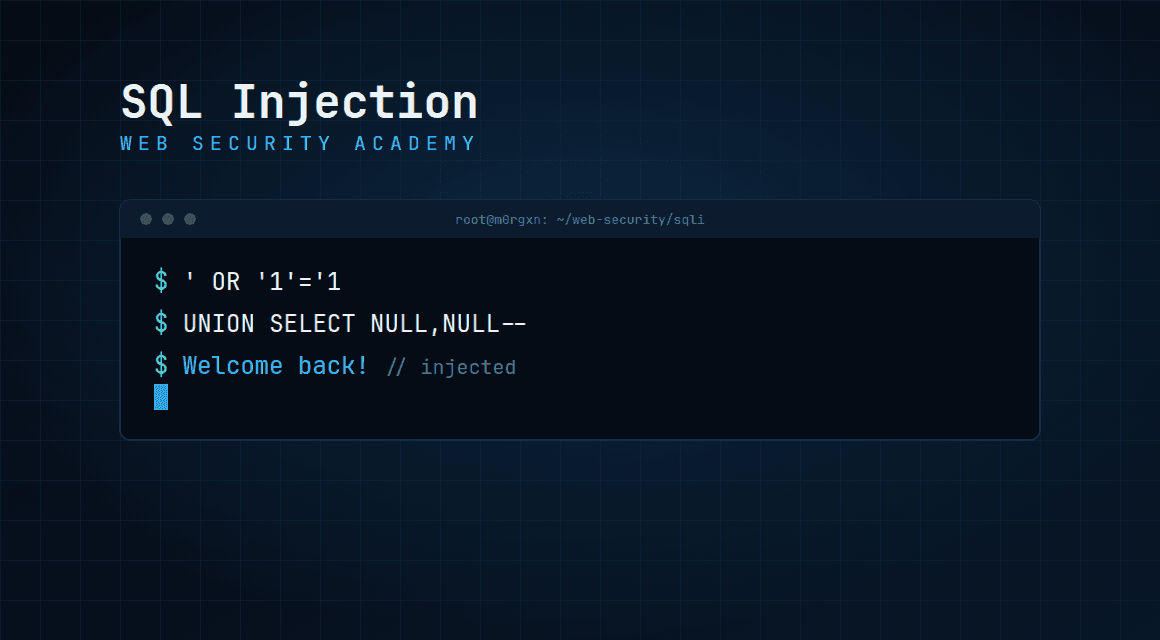
FiledSQL Injection
PortSwigger Web Security Academy notes on detecting and exploiting SQL injection, from UNION attacks to blind and out-of-band techniques
PortSwigger Web Security Academy notes on detecting and exploiting SQL injection, from UNION attacks to blind and out-of-band techniques
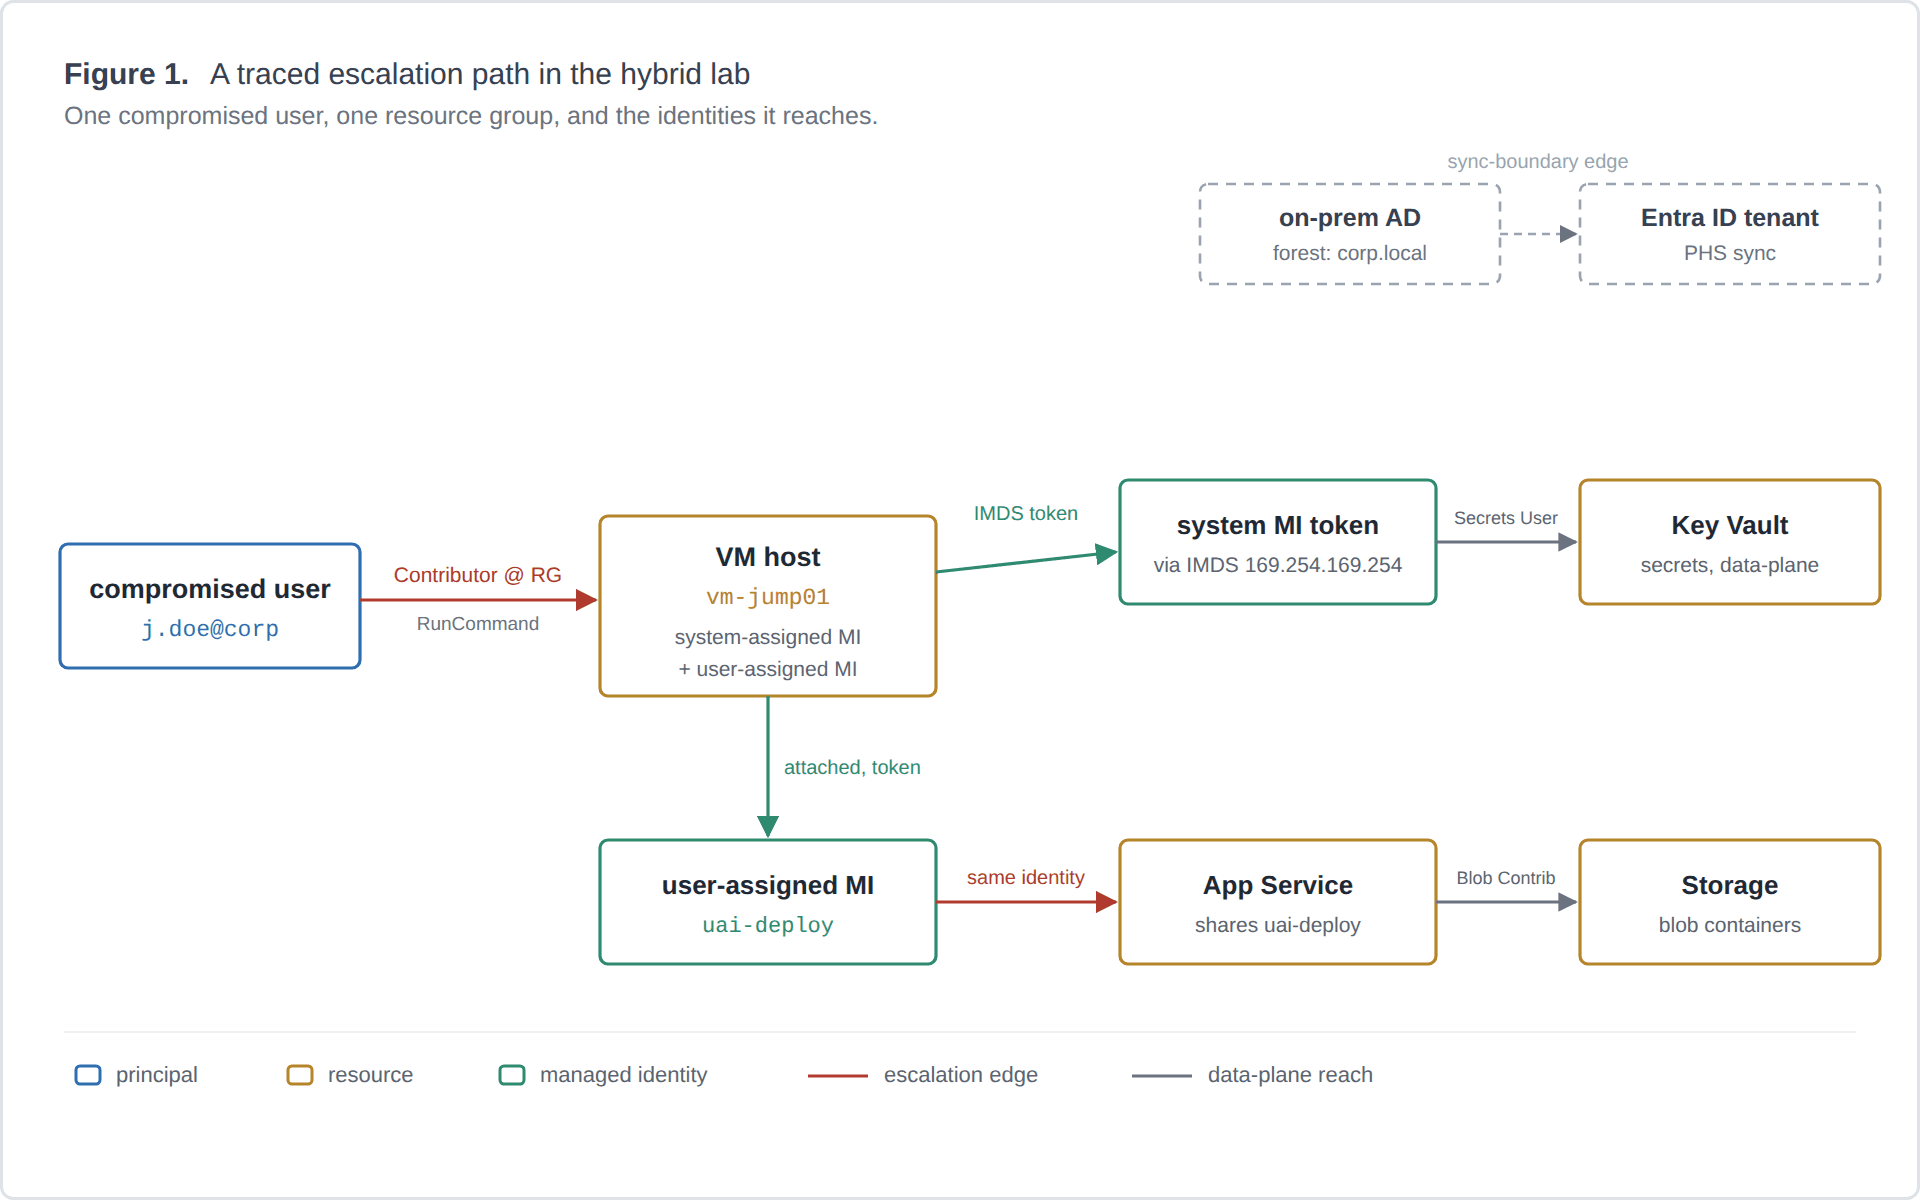
A framework for treating Azure managed-identity abuse in hybrid Entra ID environments as a graph-reachability problem. I define the node and edge types, ground each edge in Azure RBAC semantics, show how my tool Fenrir uses the model to answer one question conservatively, and work through a case study in my own lab. Framework and systematization, not an empirical study.
A walkthrough of Fenrir, a Python CLI I built during a red-team internship that automates the Azure identity attack chain: tenant recon, an exploit-readiness verdict, managed-identity token theft through compute hosts, and tenant-wide post-exploitation.
A conceptual look at the Azure Managed Identity attack surface: how App Registrations, service principals, and managed identities map onto Active Directory concepts, why the IMDS token path turns a small foothold into tenant-wide exposure, and why measuring that blast radius is worth systematic tooling.
Master shell types, reverse shells, bind shells, payload crafting with MSFvenom, and web shells for penetration testing
Advanced bash scripting techniques for security automation and penetration testing
Web fuzzing cheat sheet covering directory, page, subdomain, and parameter fuzzing with FFUF
Comprehensive guide to understanding and exploiting local and remote file inclusion vulnerabilities
Various methods for transferring files securely in penetration testing scenarios
Core cybersecurity concepts and information security principles
Deep dive into Linux kernel internals, services, and process management techniques
Exploration of server-side vulnerabilities and attack methodologies